A single ransomware incident at a 200 MW wind farm doesn't just encrypt files: it can lock out turbine controllers, trigger forced curtailment, and expose you to NERC CIP penalties before your IT team even gets a phone call. Independent power producers sit at a unique crosspoint where cyber threats translate directly into physical consequences, lost generation revenue, and regulatory liability. Standard commercial policies weren't built for this reality.
Cyber insurance tailored to independent power producers needs to account for OT systems, grid-connected events, ransomware targeting field devices, and the growing risk of physical damage caused by hacked controllers. The market for this coverage has shifted dramatically through 2025 and into 2026, with new policy forms, tighter underwriting requirements, and exclusions that can gut your protection if you're not paying attention. If you own or operate generation assets, understanding these policies isn't optional: it's a financial survival skill.
Why Independent Power Producers Face Unique Cyber Risks
Most businesses worry about data breaches and stolen customer records. IPPs face something far more consequential: attacks that cross the boundary between digital systems and physical infrastructure. A compromised SCADA server at a solar farm or a manipulated PLC at a gas peaker plant can cause equipment destruction, grid instability, and environmental incidents. The threat surface is expanding every year, and insurers are paying close attention.
CISA published over 500 Industrial Control Systems advisories in the past year alone, a 20 percent increase from 2024. That spike reflects real-world targeting of energy infrastructure, not theoretical risk.
The Intersection of IT and Operational Technology (OT)
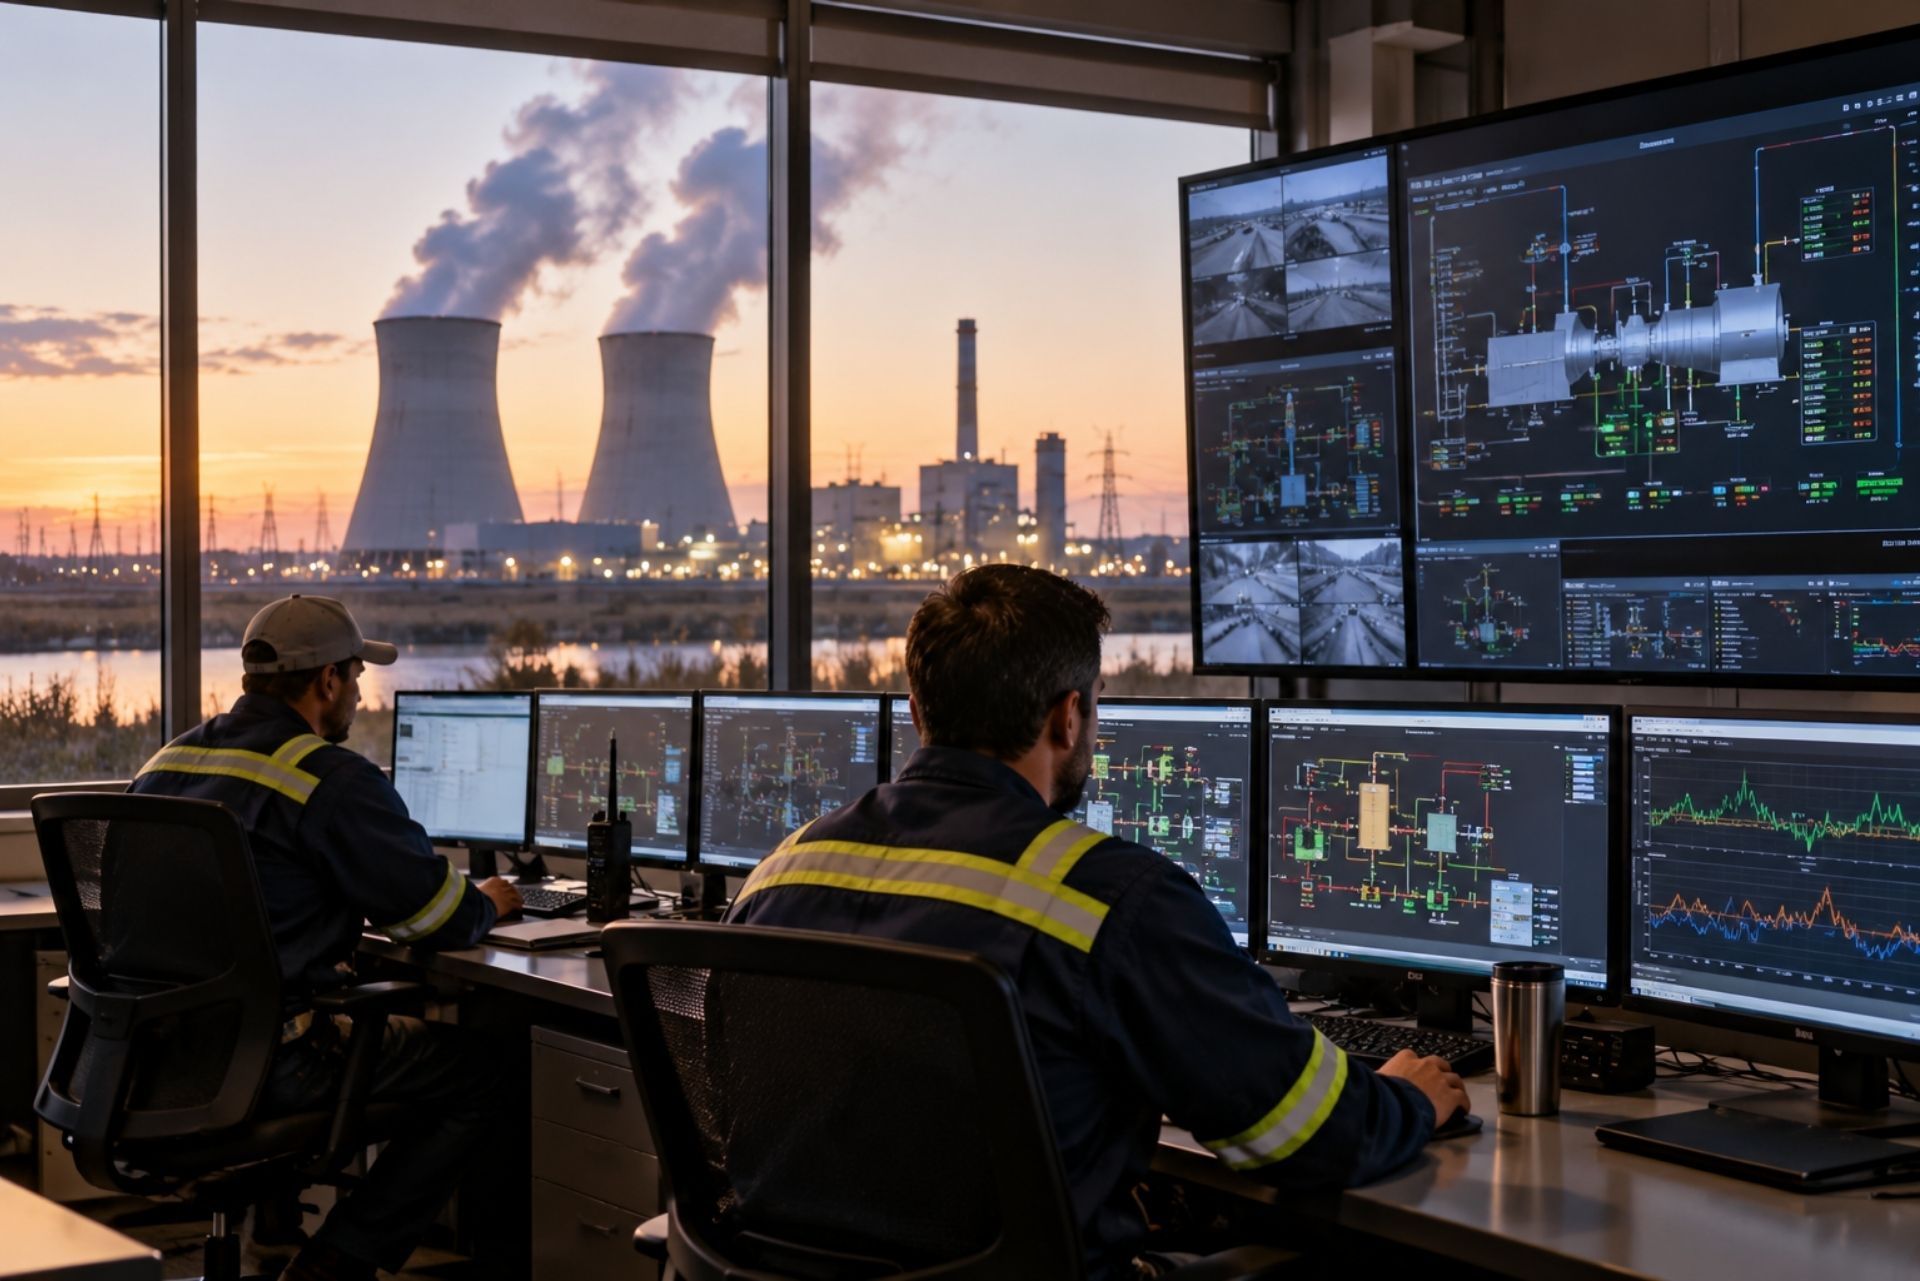
Your corporate network and your plant control systems used to be separate worlds. That's no longer true. Modern IPPs rely on cloud-based asset management, remote monitoring dashboards, and IP-connected sensors that bridge IT and OT environments. An attacker who compromises an employee's email credentials can, in poorly segmented networks, pivot into the OT layer where turbine governors, battery management systems, and breaker controls live.
Ransomware tactics have evolved to match this convergence. Threat actors now practice operational extortion by targeting Level 1 field controllers like PLCs and RTUs, threatening physical shutdowns even without encrypting data. For an IPP selling power under a tolling agreement or PPA, a forced shutdown during peak pricing hours can mean six-figure losses per day.
Supply Chain Vulnerabilities in Renewable Energy Assets
Wind turbines, inverters, and battery storage systems often ship with embedded firmware from overseas manufacturers. Patching cycles for these components lag far behind enterprise software, sometimes by years. If a vulnerability exists in a widely deployed inverter model, every site running that firmware becomes a target simultaneously.
Insurers have caught on to this accumulation risk. Many now include "unsupported software" exclusions that
deny claims if an attack exploits a known vulnerability in an end-of-life system, such as a controller running Windows Server 2012. If your SCADA host or historian database sits on unsupported OS versions, you may be paying premiums for a policy that won't pay out.
CONTACT INFORMATION
Phone
Location
9595 Six Pines Dr, Suite 8210, The Woodlands, TX 77380
Authorized to Serve Clients
BERIS International is fully licensed and permitted to sell energy, oil, and gas insurance in Texas.
We proudly serve clients across multiple states and maintain strong relationships with specialized insurance carriers to ensure that high-risk oil, gas, energy, and industrial operations receive compliant, tailored, and all-risk coverage suited to their unique exposures.
Core Coverage Components for Energy Infrastructure
A well-structured cyber policy for an IPP should address three distinct loss categories: lost revenue from network interruption, costs associated with ransomware and extortion, and regulatory exposure. Each of these deserves specific policy language, not vague references in a general cyber form.
Network Interruption and Business Income Loss
This is the coverage that replaces lost generation revenue when a cyber event forces your plant offline. The key details to scrutinize are the waiting period (often 8 to 12 hours before coverage kicks in), the indemnity period (how long the insurer will pay), and whether the trigger includes OT system compromise or only traditional IT network failures. [https://www.bloccyber.com/utility-cyber-insurance/texas]
For IPPs with merchant exposure, even a few hours of forced curtailment during a summer heat wave can dwarf the cost of the ransom itself. Make sure your policy's business income calculation accounts for real-time energy pricing, not just a flat daily rate.
Cyber Extortion and Ransomware Recovery
Global ransomware attacks hit a record 997 incidents in August 2026, with utility companies experiencing the sharpest sector increase. Extortion coverage typically pays for ransom negotiation specialists, the ransom payment itself (where legal), and the forensic and restoration costs to rebuild systems.
One common mistake: assuming this coverage handles OT restoration. Rebuilding a compromised DCS or re-flashing firmware on dozens of RTUs across remote sites is a specialized, expensive process. Confirm your policy explicitly covers OT forensics and restoration, not just IT system recovery.
Regulatory Fines and NERC CIP Compliance Costs
If you're a registered entity under NERC CIP, a cyber incident triggers mandatory reporting and potential enforcement action. Fines can reach into the millions for violations tied to inadequate security controls. A good cyber policy covers regulatory defense costs, fines where insurable by law, and the expense of hiring compliance consultants to remediate gaps identified during an investigation.
Don't overlook state-level requirements either. Several states now mandate breach notification for critical infrastructure operators on timelines as short as 72 hours. [https://www.ropesgray.com/en/insights/alerts/2024/04/new-cross-sector-72-hour-data-breach-requirements-for-critical-infrastructure]
Comparing General Liability vs. Cyber Insurance for IPPs
A persistent and dangerous misconception among IPP operators is that their existing general liability or property policy "covers cyber." It almost certainly doesn't, at least not in any meaningful way. Most GL policies contain explicit cyber exclusions, and property policies typically exclude losses caused by electronic data or software failures.
The gap becomes especially clear with physical damage caused by cyber events. A hacked PLC that causes a turbine overspeed event results in real, physical destruction, but your property insurer will likely point to the cyber exclusion. Your cyber insurer, if you have one, may point to the "bodily injury and property damage" exclusion in the cyber form. You end up in a coverage no-man's-land.
A new cyber physical damage market using risk codes CZ and CH has emerged specifically to address kinetic damage from hacked industrial controls. This is where a specialized energy insurance broker earns their fee: placing coverage across Lloyd's syndicates and surplus lines carriers who understand OT risk.
Comparison Table: Coverage Gap Analysis
| Scenario | General Liability | Standard Cyber | Energy Cyber + CZ/CH |
|---|---|---|---|
| Ransomware encrypts IT network | Not covered | Covered | Covered |
| OT attack forces plant offline | Not covered | May exclude OT | Covered with OT endorsement |
| Hacked PLC causes turbine damage | Cyber exclusion applies | Property damage excluded | Covered under CZ/CH form |
| NERC CIP fine after breach | Not covered | Often covered | Covered |
| Nation-state attack on grid | Not covered | Likely excluded under LMA5567 | Subject to "Major Detrimental Impact" threshold |
| Nation-state attack on grid |
The nation-state exclusion row deserves extra attention. The 2026 market standard uses LMA5567A/B forms that focus on a "Major Detrimental Impact" threshold rather than attacker attribution. This means your claim isn't automatically denied because a state-sponsored group was involved: the insurer evaluates whether the attack caused widespread, systemic impact beyond your facility.
Underwriting Requirements and Risk Mitigation
Getting quoted for cyber coverage as an IPP used to involve a short questionnaire. Those days are gone. Applications have evolved into 10-page technical audits requiring proof of immutable backups and endpoint detection and response tools across both IT and OT environments. If you can't demonstrate these controls, you'll either face steep premium surcharges or outright declinations.
Essential Security Controls for Lower Premiums
Underwriters in 2026 are looking for specific, verifiable controls. The following items consistently drive premium reductions:
- Multi-factor authentication (MFA) on all remote access points, including VPN connections to plant networks
- Network segmentation between IT and OT, with documented firewall rules and monitoring at the boundary
- Immutable, air-gapped backups of both IT systems and OT configurations, including PLC logic and HMI projects
- Endpoint detection and response (EDR) deployed on all Windows and Linux hosts, including SCADA servers
- Patch management program with documented timelines for OT firmware updates, even when vendor cycles are slow
- Privileged access management for any account with administrative rights to control systems
Providing engineering data, loss control reports, and maintenance histories alongside your application signals to underwriters that you take risk management seriously. This kind of documentation is often the difference between a competitive quote and a declination.
Incident Response Planning for Remote Sites
A 50-turbine wind farm spread across 15,000 acres presents different response challenges than a data center. Your incident response plan needs to account for limited on-site IT staff, cellular-only connectivity at remote substations, and the possibility that an attacker has locked out remote access entirely.
Pre-negotiate retainer agreements with OT-specialized incident response firms. Generic IT forensics shops don't know how to safely interact with live industrial control systems, and a wrong move during containment can cause the very physical damage you're trying to prevent. Your insurer will want to see this retainer documented in your application.
Tabletop exercises that simulate OT-specific scenarios, like a ransomware attack on your energy management system during peak demand, demonstrate maturity to underwriters and prepare your team for a real event.
Common Questions About Cyber Insurance for IPPs
Frequently Asked Questions
Does my property policy already cover damage from a cyberattack on plant equipment? Almost certainly not. Most property policies exclude losses originating from electronic systems or software. You need a dedicated cyber physical damage endorsement, typically placed under the newer CZ/CH risk codes, to cover scenarios like a hacked PLC causing turbine destruction.
How much does cyber insurance cost for an independent power producer? Premiums vary widely based on generation capacity, fuel type, security controls, and claims history. A 200 MW portfolio with strong OT segmentation and documented controls will price very differently from a similar-sized fleet running legacy SCADA systems. Work with a broker who specializes in energy placements to get accurate benchmarks.
Will my claim be denied if a nation-state is behind the attack? Not automatically. The current market standard evaluates whether the attack caused a "Major Detrimental Impact" at a national or systemic level. Most attacks on individual IPPs, even by state-sponsored groups, won't meet that threshold, so your coverage should respond.
What happens if we're running unsupported software on our OT systems? Insurers increasingly exclude claims tied to known vulnerabilities in end-of-life systems. If your SCADA servers run unsupported operating systems and an attacker exploits that specific weakness, your claim may be denied. Document your upgrade or compensating-control plan before your next renewal.
Do we need separate policies for IT and OT cyber risks? Not necessarily, but you need to confirm your policy explicitly covers OT environments. Many standard cyber forms were written with IT networks in mind. Look for endorsements or policy language that specifically names industrial control systems, SCADA, and field devices.
The Bottom Line for Your Power Assets
Cyber risk for independent power producers isn't a hypothetical: it's a measurable, insurable exposure that grows every quarter. The threats have moved beyond data theft into operational extortion and physical damage, and the insurance market has responded with specialized products that didn't exist two years ago.
Your priority should be threefold. First, audit your current policies for cyber exclusions in your property and GL coverage, because the gaps are likely wider than you think. Second, invest in the security controls that underwriters require: MFA, network segmentation, immutable backups, and EDR. Third, engage a specialized energy insurance broker with relationships at Lloyd's syndicates and surplus lines markets where OT-aware cyber coverage is actually written.
The IPPs that treat cyber insurance as a core part of their risk transfer strategy, not an afterthought, will be the ones that survive an incident with their balance sheet intact. Start the conversation with your broker now, before your next renewal catches you unprepared.
ABOUT THE AUTHOR: MARK BRALY
As the President and CEO of BERIS International, I’m dedicated to helping oil, gas, and energy businesses protect what matters most. With decades of experience in commercial insurance and risk management, I focus on building strong partnerships and providing reliable coverage solutions that keep high-risk operations secure across all 50 states and 185 countries.
Contact Us
Trusted by Businesses
Feedback that Reflects Service and Reliability
What Our Clients Say
Specialized Knowledge
Insurance for Energy and Oil Sectors
Focused protection for core industries
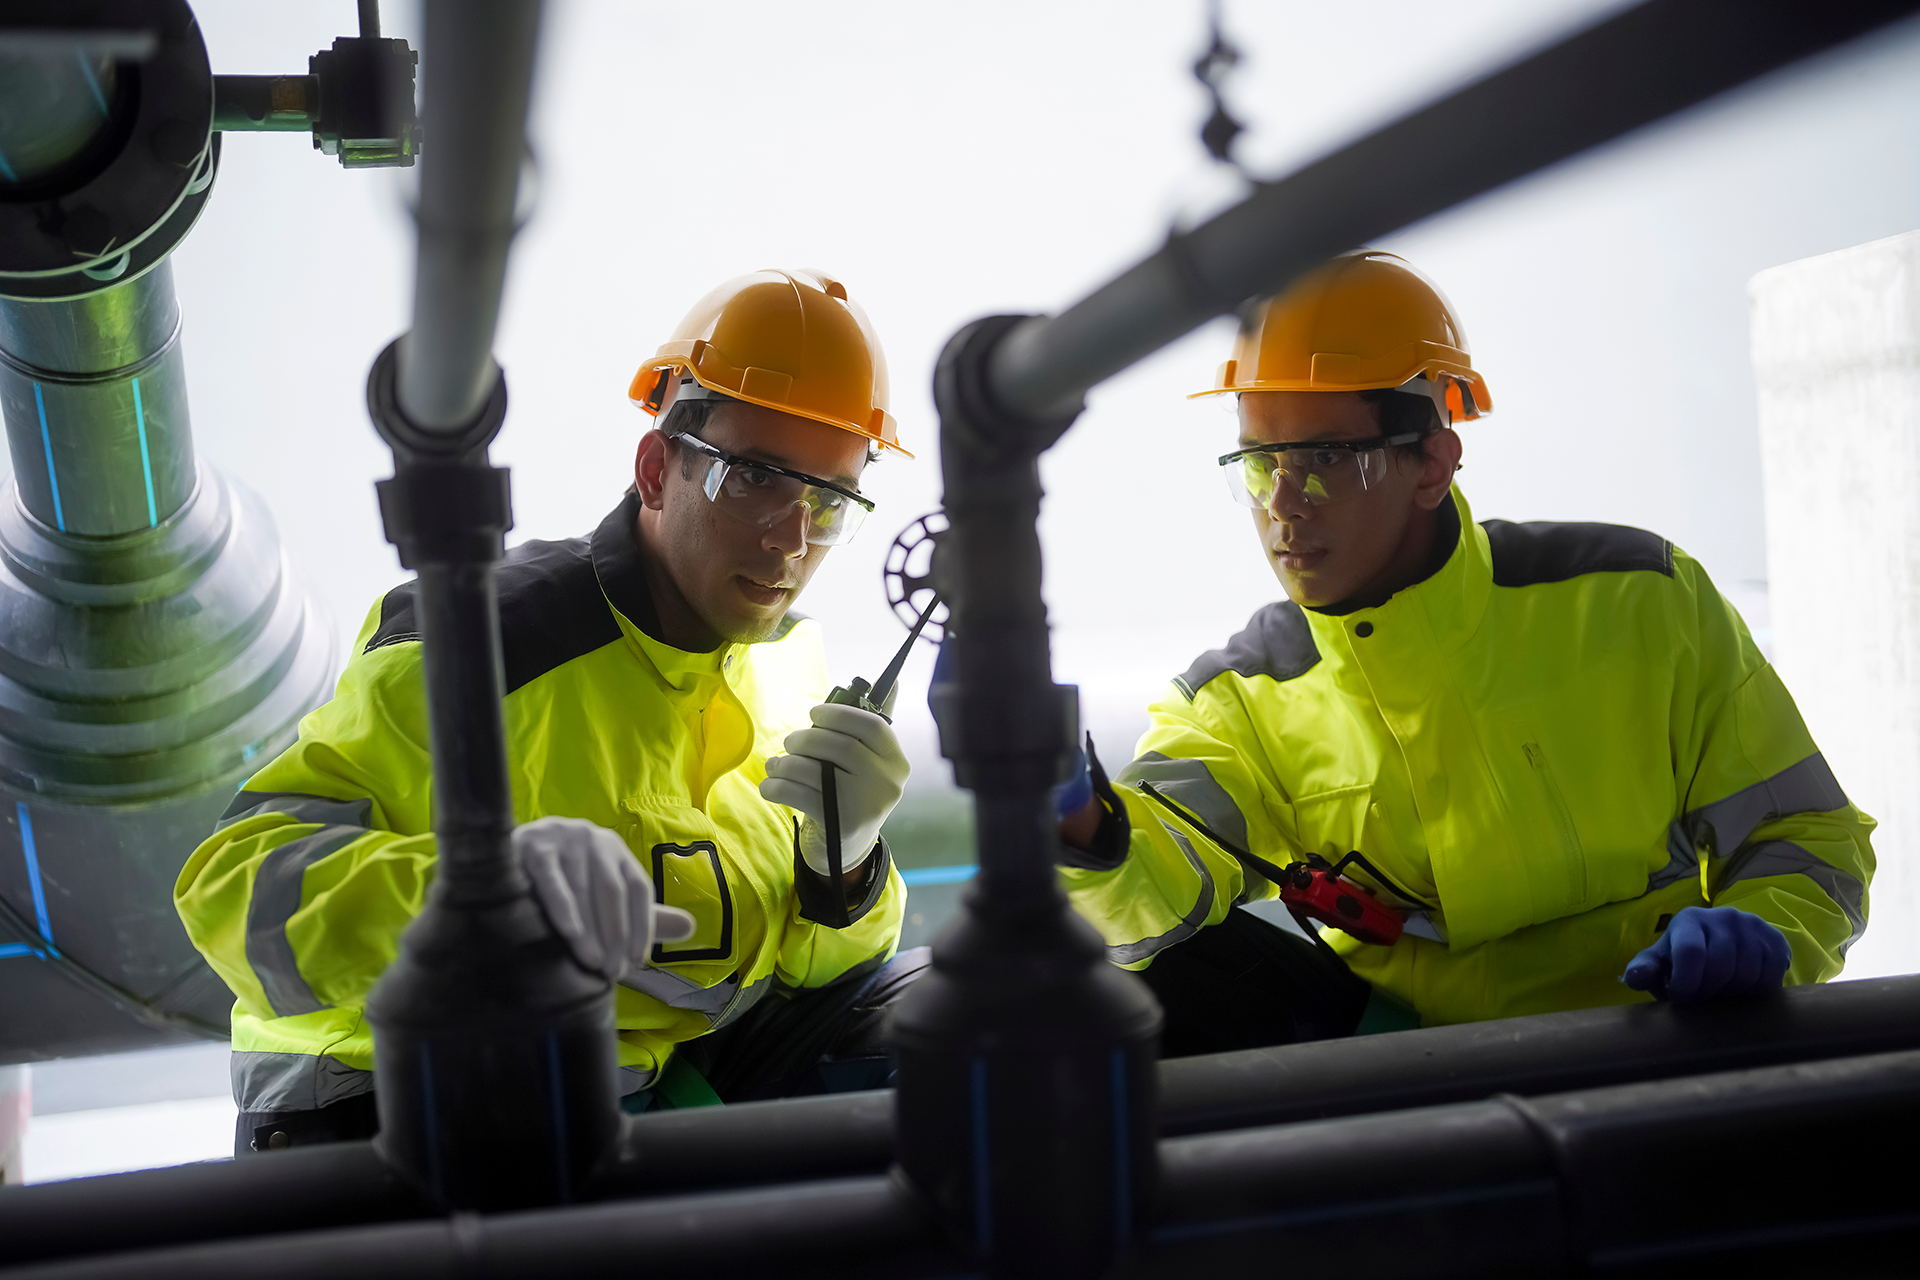
Oil Field Services
Insurance for companies supporting drilling, production, and maintenance. Protects crews, equipment, and operations from key risks.
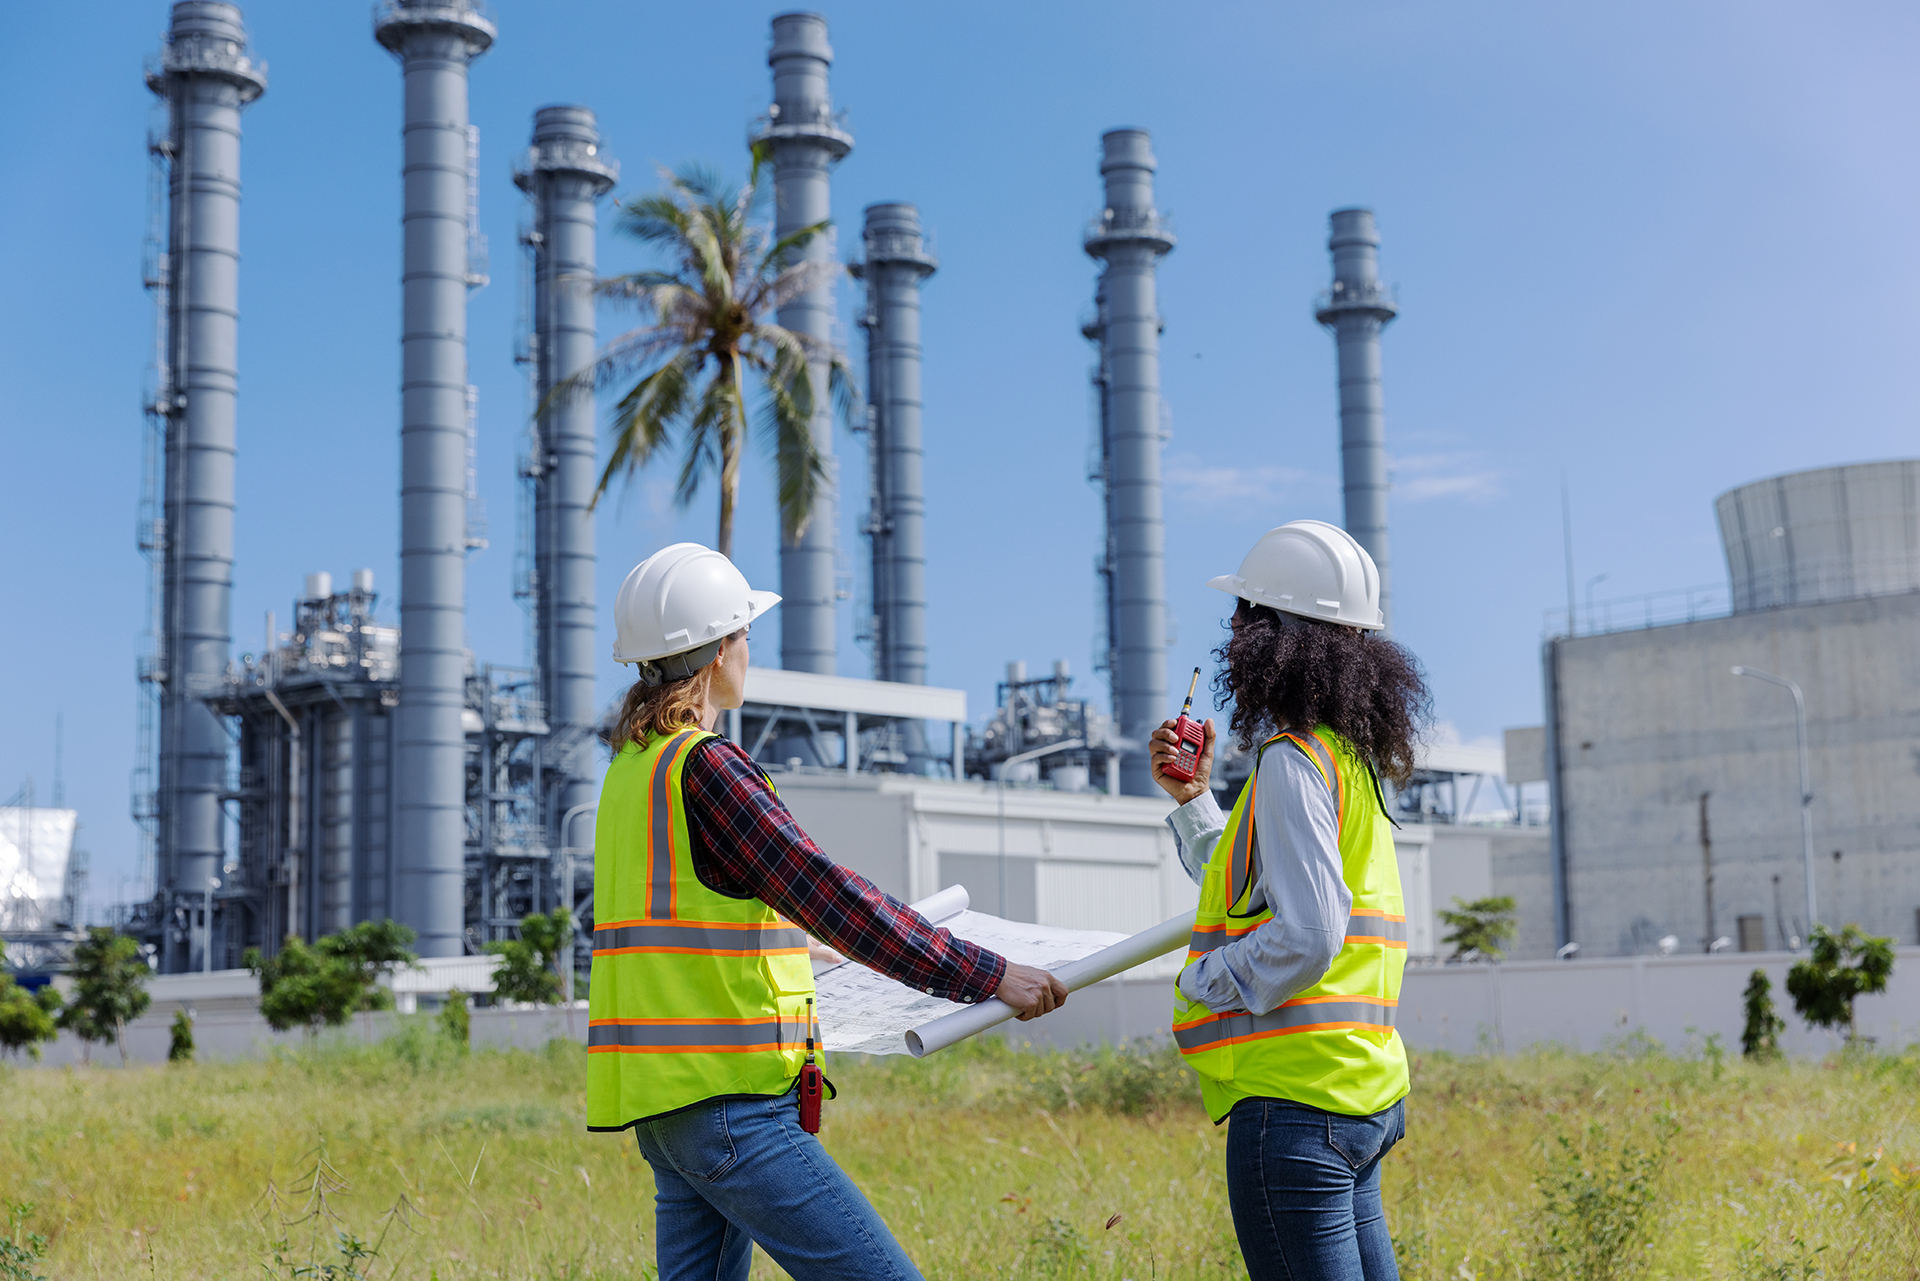
Oil Refinery Insurance
Coverage for refineries handling processing, storage, and distribution. Protects against property damage, liability, and business interruption.
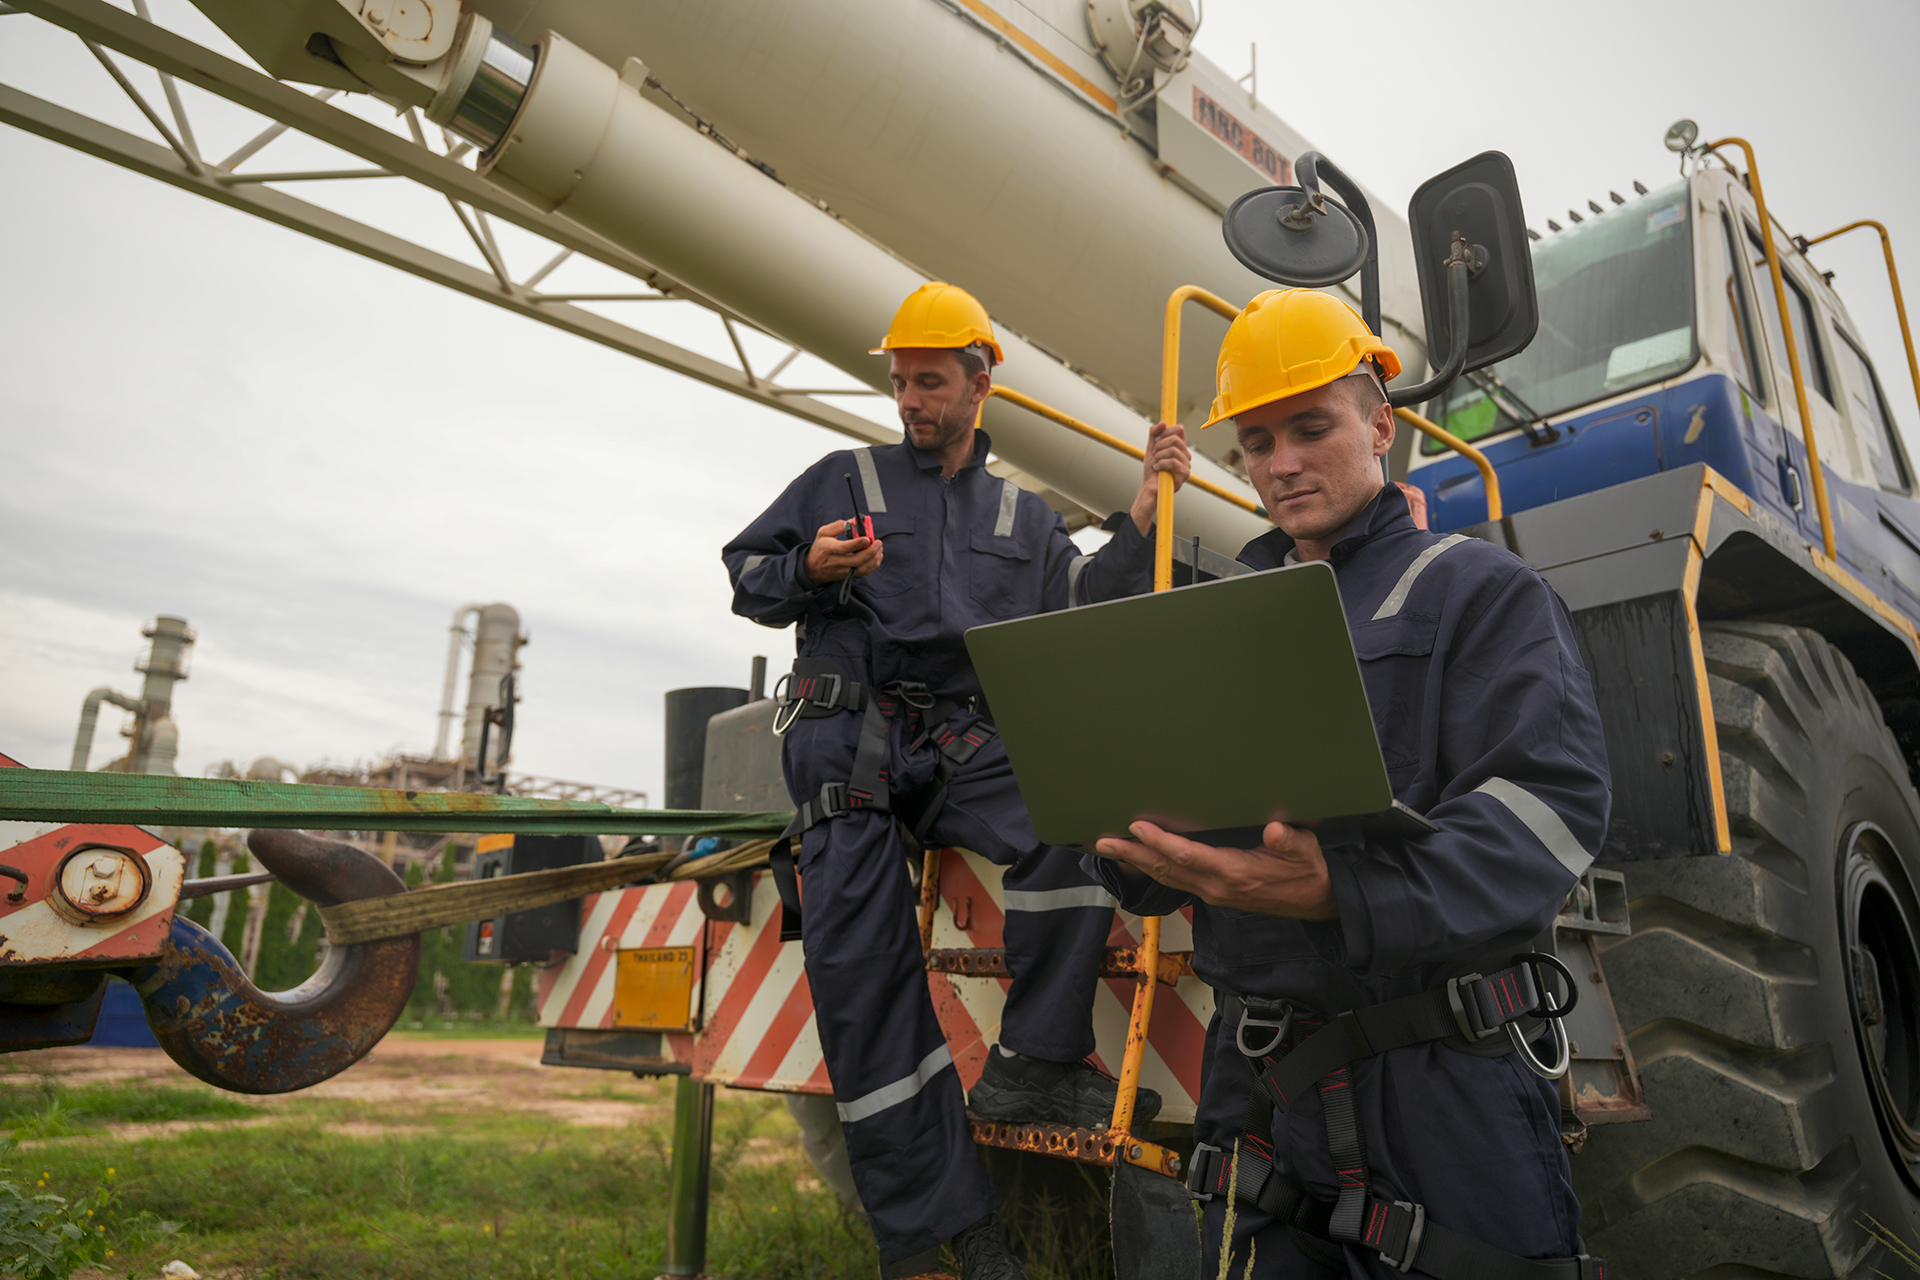
Natural Gas Pipeline Operators
Specialized insurance for natural gas operators, covering infrastructure, environmental liability, and compliance needs.
Insights That Matter
Energy and Insurance Resources
Articles designed to inform and support your business
Answers You Need
Straightforward Questions & Answers for Oil and Energy
What types of energy businesses does BERIS serve?
We support oil, gas, and energy companies, including drilling and exploration groups, pipeline operators, EPCs, service contractors, and equipment providers. Our programs scale for startups, mid-market firms, and multi-national operations.
Do you provide coverage outside the United States?
Yes. We place coverage across all 50 states and internationally in 185 countries, coordinating local documentation and endorsements so your teams can operate without delays.
Which policies are most common for energy operations?
Core coverages include General Liability, Commercial Property, Business Auto/Fleet, Workers’ Compensation, Inland Marine, and Pollution Liability. Many clients also add Excess Liability and Cyber to meet contract requirements and protect critical systems.
Can BERIS help with risk management and loss control?
Yes. We provide practical risk mitigation support, including contract review guidance, COI workflows, and safety recommendations that reduce claims and downtime.
How fast can we get a quote, and what information do you need?
Most proposals are delivered within one business day once we receive basics on operations, fleet and equipment, locations, payroll/receipts, and recent loss runs. Sharing clear details up front speeds the process and improves pricing accuracy.
What support do we get after the policy starts?
You get a direct point of contact for certificates, endorsements, audits, and claims. We monitor renewals, benchmark terms, and recommend adjustments as your projects or territories change.
Contact Us
Phone
Location
9595 Six Pines Dr, Suite 8210, The Woodlands, TX 77380